Best ISO 27001 Compliance Software (2026): 9 Tools Graded on ISMS Documents, Risk Assessment, and the Certification Body
Most "best ISO 27001 software" lists are written by the vendors on them, and most of those vendors started out as SOC 2 tools. That matters, because an ISO 27001 certification auditor isn't mainly checking your cloud configuration. They're checking a management system: a documented scope, a risk assessment method you actually follow, a Statement of Applicability, an internal audit, and a management review. Clauses 4–10 of the standard decide whether you pass. Annex A is only part of the test.
This guide is for teams that have already decided to certify. (If you're still choosing between frameworks, start with our breakdown of ISO 27001 vs SOC 2 and which to get first.) We graded nine platforms on the three jobs a first-time ISO program actually struggles with: writing the ISMS documents, running the risk assessment, and getting through an accredited certification body. We used each vendor's own documentation and listed prices as of October 2026.
If ISO 27001 is your only framework this year, you don't need a $14,000 SOC 2 platform. If ISO is the first of several, you probably do.
Hicomply — best ISMS-native platform with evidence automationBuilt around Clauses 4–10 rather than retrofitted, publishes its price ($6,995/yr Essentials, unlimited users), and still connects to 75+ tools for evidence.
Conformio — best value for a first certification on a small budget$1,399–$2,699/yr, ships every mandatory ISO document, including the internal audit and management review records that SOC 2-first tools tend to leave to you. No cloud monitoring.
Drata or Vanta — best when ISO 27001 sits next to SOC 2From $15,000 and $14,000 a year respectively on AWS Marketplace. Strongest automated evidence collection, but you'll write more of the ISMS layer yourself.
§4–10Why ISO 27001 changes the shortlist
Compliance automation platforms are sold on control monitoring: connect AWS, Okta and GitHub, watch tests turn green. That's most of the work for SOC 2. ISO/IEC 27001:2022 adds a layer that monitoring can't produce. In Sprinto's own summary, the first three clauses are scope and terminology, and "Clauses 4–10 contain the auditable requirements, plus Annex A, which contains 93 controls grouped under 4 themes."
Map those clauses to what software can actually do, and three gaps show up:
- Clause 4 (context and scope). Nobody's API knows which business units, sites and contractors sit inside your ISMS. That's a document you write, and the 2024 amendment added that you must "determine whether climate change is a relevant issue" (ISO/IEC 27001:2022/Amd 1:2024).
- Clause 6.1 (risk assessment and treatment). You need a repeatable method (assets, threats, likelihood, impact, owners) and a treatment plan that ties back to the Statement of Applicability. Tools vary from a full asset-threat-vulnerability catalog to a blank register.
- Clause 9.2 and 9.3 (internal audit and management review). Both are mandatory, and both must leave records. Many platforms offer a checklist here, not a workflow, and the internal audit has to be performed by someone independent of the work being audited.
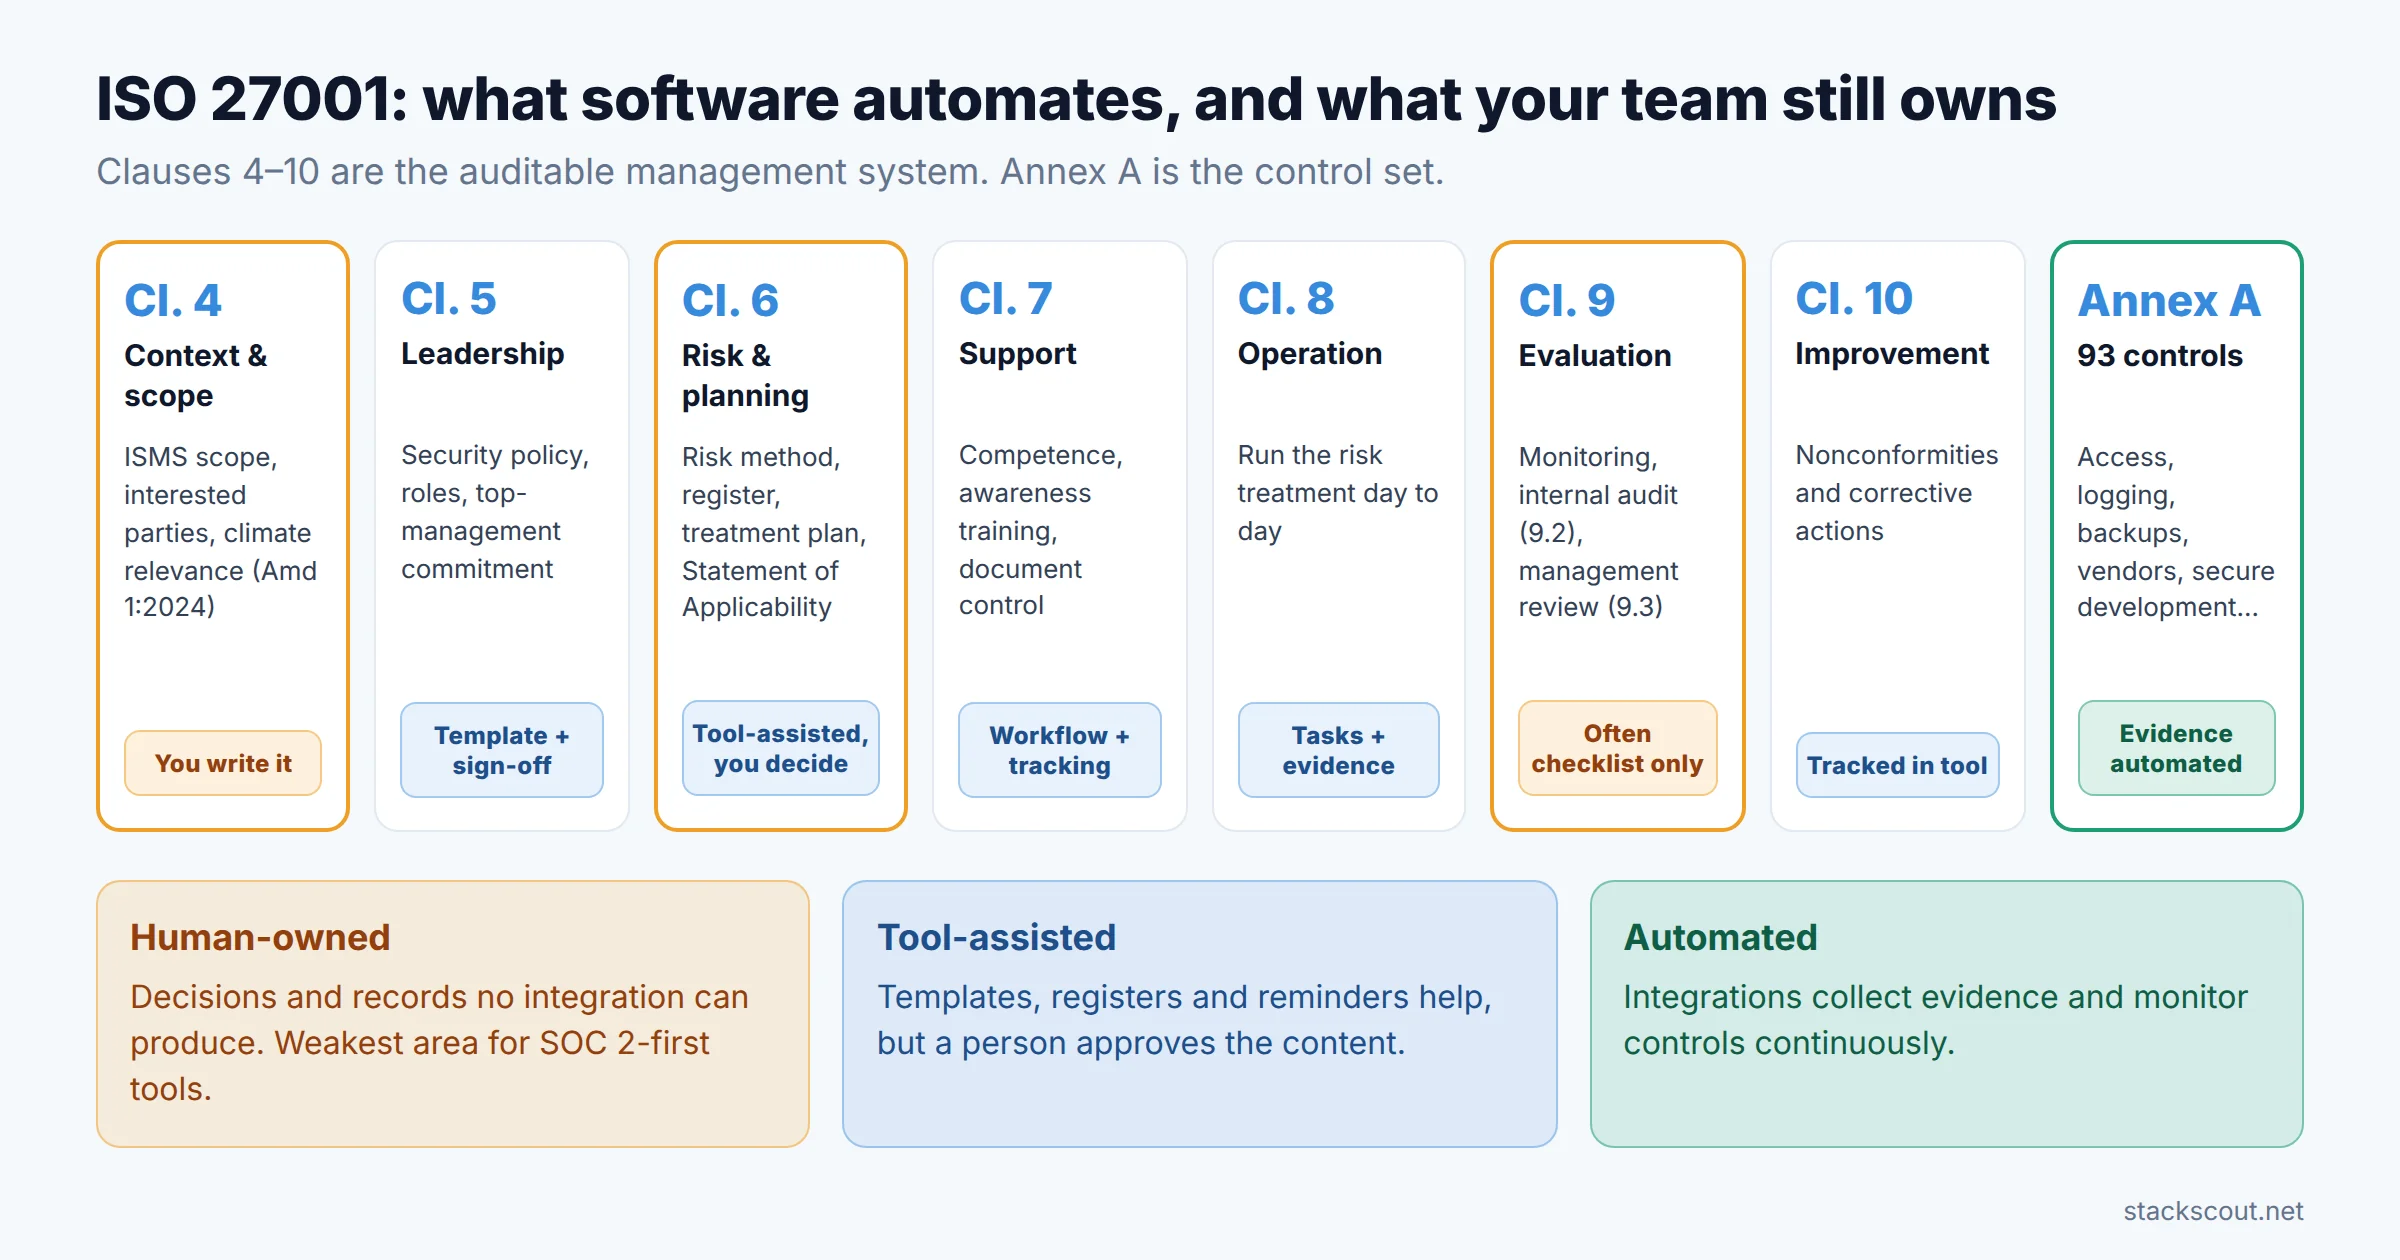
That's why the ranking below doesn't follow integration counts. A platform with 400 integrations and a blank management-review page can leave a first-time team further from certification than a $1,399 document tool. If what you're really after is a general compliance stack for a seed-stage company, our compliance automation picks for early-stage B2B SaaS covers that broader question.
TableThe 9 tools side by side
Prices come from each vendor's public pricing page or its AWS Marketplace listing (the only place several of them publish numbers), checked October 2026 unless noted. AWS Marketplace prices are 12-month list prices. Negotiated contracts are often different.
| Tool | Built as | Lowest published price | ISMS documents | Risk assessment | Certification audit route |
|---|---|---|---|---|---|
| Hicomply | ISMS-native | $6,995/yr | Policy center, ISMS scoping | Built-in risk module | Invite your own auditor |
| Conformio | ISO document wizard | $1,399/yr | All mandatory docs incl. internal audit & management review | Asset/threat/vulnerability catalog | Your own CB (pre-audit check on Advanced) |
| ISMS.online | ISMS-native | Bespoke (not published) | "Headstart" pre-built content | Dynamic risk register | Your own CB |
| Vanta | SOC 2-first, multi-framework | $14,000/yr* | Templates; SoA template/upload | Risk module | Auditor network / your own CB |
| Drata | SOC 2-first, multi-framework | $15,000/yr* | Templates | Risks linked to controls | Auditor network / your own CB |
| Secureframe | SOC 2-first, multi-framework | $15,000/yr* | Templates vetted by former auditors | Generated risk register | Partner auditors / your own CB |
| Sprinto | Multi-framework | $9,500/yr* | Mandatory docs pre-drafted; SoA pre-filled | Risk module | Your own CB |
| Scytale | Multi-framework + services | $7,500/yr* | Templates + compliance expert | Risk module | Built-in audit bundle (from $4,200) |
| Thoropass | Platform + own certification body | $8,700/yr* (Sep 2026) | Not detailed publicly | 5×5 risk register linked to controls | Thoropass Certification LLC (IAS-accredited) |
*AWS Marketplace list price. Vanta: Essentials package, 1–20 employees. Drata: Foundation package, 1–50 FTE. Secureframe: $7,500 platform (up to 100 employees) + $7,500 first framework. Sprinto: $7,500 Starter platform (up to 100 employees) + $2,000 first framework. Scytale: $7,500 incl. one framework, "starting price, get quote." Thoropass: platform list price checked September 2026; the ISO audit fee is not published.
ISMS coverage, clause by clause
This is the grid most comparison pages skip. A green dot means the vendor documents a dedicated workflow, module or document for that clause. Amber means you get a template, checklist or guidance article but run the process yourself. Grey means we found nothing in the vendor's public documentation. It doesn't mean the feature can't exist; it means you should ask for a demo of it.
| Tool | Cl. 4 scope | Cl. 6.1 risk | SoA | Cl. 9.2 internal audit | Cl. 9.3 mgmt review | Annex A evidence automation |
|---|---|---|---|---|---|---|
| Hicomply | Scoping tool | Module | Guidance | Guidance | Guidance | 75+ integrations |
| Conformio | Scope document wizard | Catalogs + Annex A suggestions | Wizard | Program + report | Minutes template | None listed |
| ISMS.online | Headstart content | Dynamic register | Headstart content | Guidance | Guidance | Secondary focus |
| Vanta | Template | Module | Template; status set manually | Checklist | Checklist | Strong |
| Drata | Template | Risks linked to controls | Guidance | Guidance | Guidance | Strong |
| Secureframe | Template | Generated register | Template | Guide | Not found | Strong |
| Sprinto | Pre-drafted | Module | Pre-filled from stack | Guidance | Guidance | Strong |
| Scytale | Expert-assisted | Module | Expert-assisted | Via consulting package | Via consulting package | Strong |
| Thoropass | Not found | Risk register | Not found | Not from its CB arm | Not found | Strong |
ReviewsThe 9 platforms, reviewed
1. Hicomply
Hicomply is one of the few platforms here that was designed around the management system first and the integrations second. That shows in the product menu: a dedicated ISMS scoping tool ("define and document your ISMS"), an information-asset inventory, a risk module, and policy templates. All of that sits alongside cloud control monitoring, AI evidence discovery and, per the vendor, connections to 75+ tools.
The pricing is unusually transparent for this category. The US plans page lists Essentials from $6,995 a year and Professional at $13,995 (£5,300 and £10,600 in the UK). Every tier includes unlimited users "within fair use (up to 500 employees)", so the price doesn't climb as you add control owners. That matters more for ISO than for SOC 2, because ISO risk ownership tends to be spread across department heads.
The trade-off is ecosystem depth. 75+ integrations is plenty for a typical AWS/Google Workspace/Jira stack, but it's well short of the large US platforms. Its roots are in the UK: the framework list includes UK-specific schemes such as Cyber Essentials, NHS DSPT and the NCSC CAF, which helps if you sell into the UK public sector.
Pros
- Clause 4 scoping and asset inventory built in
- Published, flat pricing with unlimited users
- Covers ISO 27701, 42001 and 9001 for integrated management systems
Cons
- Smaller integration library than Vanta or Drata
- Internal audit and management review are guidance, not workflow
- Less brand recognition with US enterprise buyers
2. Conformio (Advisera)
Conformio is the honest outlier on this list. It doesn't monitor your cloud at all, and its pricing page lists no integrations. It's a guided ISMS documentation and project tool from Advisera, a company that has sold ISO 27001 document toolkits for years. What you get is the thing SOC 2-first platforms are weakest at: every mandatory ISO 27001 document, written through wizards in an online editor.
The mandatory-document list on its pricing page reads like an auditor's Stage 1 checklist: ISMS Scope, Information Security Policy and Objectives, Risk Assessment and Treatment Methodology and Report, Statement of Applicability, Risk Treatment Plan, Internal Audit Program, Internal Audit Report, Management Review Minutes and Corrective Action Form. The risk register comes with catalogs of assets, threats and vulnerabilities and "automatically suggests appropriate controls from Annex A". A maintenance module creates recurring tasks so the ISMS doesn't go stale between surveillance audits.
Pricing, from Advisera's page in October 2026: Starter $1,399/yr (3 users, up to 100 risks), Professional $2,399/yr (5 users, unlimited risks, awareness training for 20 employees) and Advanced $2,699/yr (unlimited users, awareness training for 50, an hour of expert consultation and one document review per month, plus a 2-hour pre-audit check). There's a 14-day free trial.
The catch is labor. You'll collect Annex A evidence by hand: screenshots, exports, access reviews. That's manageable for a 15-person company with a simple stack and painful for a 150-person one.
Pros
- Covers Clauses 4–10 records end to end, including 9.2 and 9.3
- Lowest published price by a wide margin
- Expert review and pre-audit check on Advanced
Cons
- No automated evidence collection or control monitoring
- Starter caps the register at 100 risks
- Weak fit if SOC 2 is coming next year
3. ISMS.online
ISMS.online is the longest-standing ISMS-native platform in this group, and it remains closest to how ISO consultants think. Its plans page highlights three pieces that do the Clause 4–10 heavy lifting: "Headstart" pre-built content (policies and controls), the Assured Results Method (ARM), a step-by-step implementation path, and a Virtual Coach. The platform's own material emphasizes a dynamic risk register and Stage 1/Stage 2 audit preparation.
Its strength is integrated management systems. The case studies on its site include companies running ISO 27001 alongside ISO 9001 and 45001 in one platform, and an early ISO 42001 (AI management) certification. If your quality or AI governance team also needs an ISO system, sharing one document-control and internal-audit backbone is a real saving.
The pricing page no longer shows numbers. It now offers "bespoke plans" built from a base plan plus marketplace add-ons and extra standards. Older per-month figures still circulate on review sites, so treat them as stale and get a quote. Evidence automation exists but isn't the product's center of gravity.
Pros
- Deep ISO-native content and guided method
- Strong for integrated ISO 27001 + 9001 + 42001 systems
- Case studies include audits with UK certification bodies such as Alcumus ISOQAR
Cons
- No public pricing
- Less automated evidence than US platforms
- Interface is document-heavy
4. Vanta
Vanta's AWS Marketplace listing shows the Essentials package at $14,000, Plus at $21,500 and Professional at $23,000, all "starting cost for 1–20 employees." The Trust Center module adds $6,000. Which frameworks each package includes depends on the quote, so confirm ISO 27001 is in yours.
Where Vanta is strong is the part SOC 2 and ISO share: continuous tests mapped to Annex A, and an "Audits" workspace for auditor collaboration. On the ISMS side, its help center is candid about what's manual. The Statement of Applicability article tells you to "upload your version or use a prebuilt template," then fill in each control's status (implemented, excluded, in-process, not started) yourself, using the related tests as a guide. Vanta also publishes an ISO 27001:2022 management review checklist (Clause 9.3) and an internal audit checklist written with BD Emerson. Those are useful, but they're checklists, not a workflow that produces the records for you.
Read that as: Vanta automates Annex A evidence very well and gives you good scaffolding for Clauses 4–10, but someone still writes the ISMS. Teams that already run Vanta for SOC 2 will find adding ISO relatively cheap in effort. Teams that only need ISO are paying for monitoring depth they may not use in year one.
Pros
- Best-in-class evidence automation and test library
- Large auditor network and strong buyer recognition
- Good published ISO checklists for 9.2 and 9.3
Cons
- SoA status is maintained manually
- High entry price for an ISO-only program
- Add-ons (Trust Center, TPRM) raise the total quickly
5. Drata
Drata's AWS listing has one public price: the Foundation package at $15,000 for 1–50 FTE companies. Its ISO 27001 product page is notably written for year two and three, not just the first audit. It talks about reusing evidence "across surveillance audits," preserving historical evidence for recertification cycles, and linking "ISO 27001 risk assessments directly to controls and supporting evidence."
That risk-to-control link is the most ISO-relevant thing Drata does. An auditor sampling your risk treatment plan wants to trace a risk to the control that treats it and to the evidence that the control works. Drata keeps that chain in one place. Vendor and supplier risk also feeds into the same view, which helps with Annex A 5.19–5.22 (supplier relationships).
Like Vanta, Drata leaves the Clause 4 scope, internal audit and management review largely to you, with guidance content rather than dedicated workflows. If you're weighing the two, our Vanta-to-Drata migration guide covers the switching math and what doesn't carry over.
Pros
- Risk → control → evidence traceability
- Explicit support for surveillance and recertification evidence history
- Strong multi-framework mapping
Cons
- Highest published entry price here
- Clauses 4 and 9 still largely self-run
- Per-framework pricing above Foundation not published
6. Secureframe
Secureframe's AWS listing splits the price cleanly: $7,500 for platform access up to 100 employees plus $7,500 for the first framework, "choice of any framework." For an ISO-only buyer that makes it $15,000, the same as Drata's entry point, but with a higher employee ceiling.
Its most ISO-useful feature is the risk module. Secureframe says that once you answer questions about your environment, the platform generates a risk register you can then monitor and treat, which beats starting Clause 6.1 from a blank sheet. Its policy templates are described as "developed and vetted by in-house security experts and former auditors," and its ISO 27001 page lays out the full certification lifecycle correctly: Stage 1 document review, Stage 2 controls review, a 3-year certificate, and two surveillance audits.
Secureframe's framework list (ISO 27701, NIST 800-53 and 800-171, CMMC, FedRAMP) makes it a reasonable pick if federal work is on your roadmap. For management review we found no dedicated feature in its public material, so plan to run Clause 9.3 outside the tool or ask to see it in a demo.
Pros
- Questionnaire-generated risk register
- Transparent platform + framework price split
- Broad framework catalog incl. CMMC and NIST
Cons
- Same entry cost as Drata for ISO-only
- Management review not evident in public docs
- Each extra framework adds cost
7. Sprinto
Sprinto's main AWS listing prices the Starter platform at $7,500 (up to 100 employees) plus $2,000 for the first framework, with ISO 27001 explicitly on the list. That makes it the cheapest automation-first route to ISO here at $9,500.
On the ISMS layer, Sprinto says it "ships with every mandatory document pre-drafted, pre-fills your SoA against the controls your actual tech stack needs," and keeps policies version-controlled. Pre-filling the SoA from detected infrastructure is a genuine time saver. The justification column for each of the 93 controls is where first-time teams often stall. Just review it critically. A tool can tell you that you run on AWS. It can't decide your risk appetite, and auditors do ask why a control was excluded.
Sprinto's ISO guide also includes a section on "picking the right ISO 27001 auditor," noting that "your certification is only as credible as the body that issues it." That's the right instinct, and we cover how to check accreditation below.
Pros
- Lowest automation-first entry price
- SoA pre-filled from your tech stack
- Mandatory documents pre-drafted
Cons
- Pre-filled SoA still needs human justification
- Second AWS listing shows different term pricing, so get a written quote
- Less suited to non-cloud or physical-site-heavy scopes
8. Scytale
Scytale prices like a hybrid of software and consultancy. Its AWS listing starts the platform at $7,500 including one framework ("starting price, per org size, get quote"), then lists service packages: an additional framework from $2,100, framework consulting from $4,000, penetration testing from $4,500, and third-party audit services from $4,200.
For ISO that service layer is the point. A dedicated compliance expert can draft the scope, the risk method and the SoA with you, which partly offsets the ISMS-layer gap of automation tools. Scytale also says it will "connect you with the right auditor based on your industry, company size, and timeline," with bundle pricing through its Built-In Audit program.
Two cautions. First, $4,200 is a starting price, and ISO certification audit time is set by headcount (see the next section), so a 100-person company won't pay the floor. Second, check that the certification body you're introduced to is accredited for ISO/IEC 27001 by an IAF MLA signatory. A bundle is only a saving if the certificate will satisfy your customers.
Pros
- Expert services fill the Clause 4–10 gap
- Audit, pentest and platform under one vendor
- Low published entry price
Cons
- Service add-ons push total cost up fast
- All prices are "starting from"
- You must vet the introduced auditor's accreditation
9. Thoropass
Thoropass is the only vendor here with its own accredited ISO certification body. Thoropass Certification LLC holds IAS accreditation MSCB-422, effective August 17, 2026, to certify ISMS against ISO/IEC 27001:2022 under ISO/IEC 27006-1:2024. IAS describes itself as an IAF MLA signatory, which is what makes a certificate recognized internationally. The accreditation is only two months old, so expect a short track record.
The structure has a built-in guardrail you should understand before you buy. Thoropass's impartiality policy states that its certification arm "does not provide management system consultancy or internal audit services to certification clients." That's the ISO/IEC 17021-1 rule working as intended. It also means you'll need a separate internal auditor for Clause 9.2. Don't assume the "one vendor" promise covers it.
The platform starts around $8,700 a year on AWS Marketplace (checked September 2026). Thoropass doesn't publish its ISO certification audit fee. The appeal is coordination: one calendar, one evidence repository, and an auditor who already sees your controls in the tool. The risk is concentration. If the relationship sours, you change platform and certification body at the same time, mid-cycle.
Pros
- Platform + IAS-accredited certification body
- 5×5 risk register linked to controls
- Clear, published impartiality and appeals process
- Also handles SOC 2 through an affiliated CPA practice
Cons
- ISO accreditation only since August 2026
- Internal audit must come from someone else
- Switching later means changing both tool and CB
Considered and excluded. Hyperproof and LogicGate are capable GRC platforms but are quote-only and aimed at larger risk programs rather than a first certification. Delve was excluded after the 2026 whistleblower allegations of fabricated evidence and its split from Y Combinator. Open-source options such as Comp AI (AGPL-3.0) are worth a look if you have engineers to spare, but expect to write the ISMS layer yourself.
CBThe part no software does: the certification body
Every tool above prepares you for an audit. None of them is the audit, apart from Thoropass's separate certification entity. ISO itself doesn't certify anyone. As iso.org puts it, holding a certificate "from an accredited conformity assessment body may bring an additional layer of confidence." Here's how coordinating with a certification body (CB) actually works, and where software helps.
1. Verify accreditation before you sign
Ask for the CB's legal entity name and its accreditation body. In the US that's typically ANAB or IAS; in the UK, UKAS; in Germany, DAkkS. Then confirm ISO/IEC 27001 is inside that accreditation scope. After certification, your certificate should be findable in IAF CertSearch, which shows the standard, scope, status, CB and accreditation body. Unaccredited "certificates" are still sold, and enterprise procurement teams increasingly check.
2. Know how audit days are calculated, because that's the price
CBs price by audit days, and audit days come from a table in ISO/IEC 27006 driven by the number of people in your ISMS scope. ISO/IEC 27006-1:2024 widened that headcount to people working under your control "regardless of whether they are members of the organization or not," so in-scope contractors and freelancers now count. Its transition period ended March 31, 2026, so every audit starting after that date uses the new rules.
IT Governance budgets a typical day rate of £1,250, which puts a 16–25 person company at about £8,750 for the initial audit and a 46–65 person company at about £12,500. Day rates vary a lot by CB and region, but the day count is the lever you can actually check. If a quote's day count looks far below the table, ask why; if it looks far above, ask what complexity factor they applied.
3. Plan the three-year cycle, not just the first audit
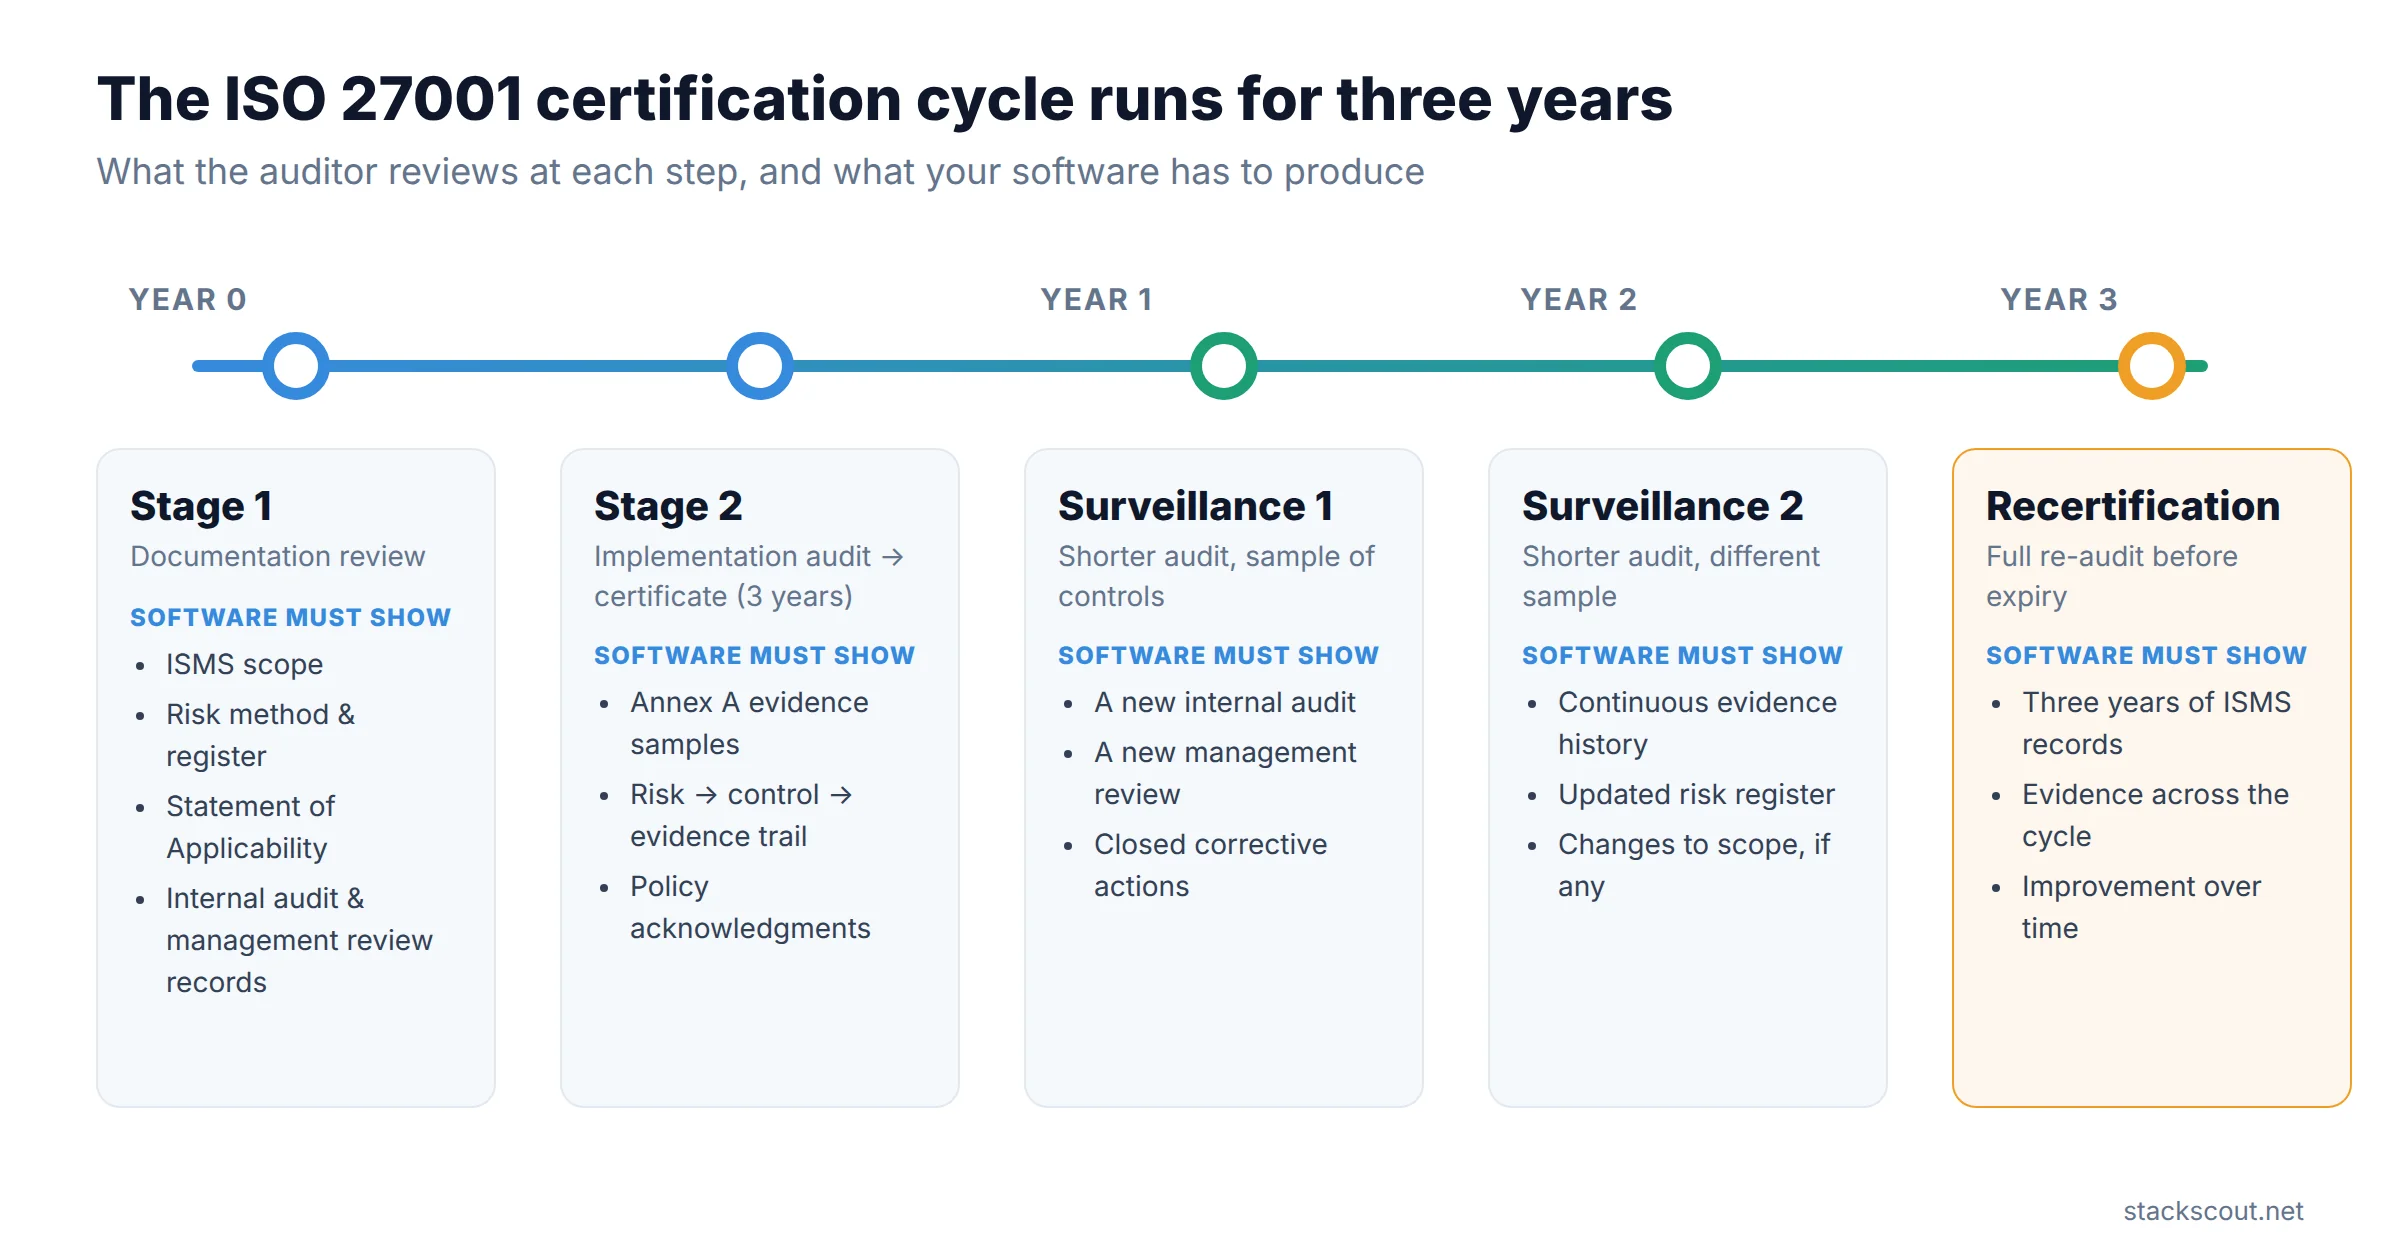
- Stage 1 (documentation review). The auditor reads your scope, risk method, SoA, policies, and internal audit and management review records. This is where Conformio-style document completeness pays off, and where SOC 2-first teams most often get findings.
- Stage 2 (implementation audit). The auditor samples controls and evidence. Automated evidence (Vanta, Drata, Secureframe, Sprinto) shortens this considerably.
- Surveillance audits, years 1 and 2. Shorter audits on a sample of controls, plus proof that the ISMS ran: a new internal audit, a new management review, closed corrective actions. Many CBs quote these at roughly a third of the initial fee. Treat that as a rule of thumb, not a fixed rate.
- Recertification, year 3. A full re-audit before the certificate expires. Drata's evidence history and Conformio's maintenance reminders target exactly this stage.
Already on SOC 2? The audit calendars don't line up neatly: a SOC 2 Type 2 report covers an observation window, while ISO runs on surveillance dates. Our SOC 2 Type 1 vs Type 2 calendar guide shows how to sequence the two so one evidence period serves both.
$What year one actually costs: three scenarios
Software plus certification body, using only the published figures above. Internal staff time, penetration testing and any consultant are extra, and they're often the largest line. Currencies are left as published rather than converted.
| Scenario | Software (list) | Initial CB audit | Who it suits |
|---|---|---|---|
| A. 20 people, ISO only, hands-on founder | Conformio Professional $2,399 | 7 days ≈ £8,750 at £1,250/day | Simple cloud stack, no SOC 2 planned within 12 months |
| B. 20 people, ISO now, more frameworks later | Hicomply Essentials $6,995 or Sprinto $9,500 | 7 days ≈ £8,750 | Wants evidence automation without SOC 2-platform pricing |
| C. 50 people, ISO + SOC 2 this year | Drata Foundation $15,000 or Secureframe $15,000 | 10 days ≈ £12,500, plus a SOC 2 CPA fee | Engineering-led evidence, US enterprise buyers |
CB figures use IT Governance's illustrative £1,250 day rate and the ISO 27006 day table; real quotes vary by CB, region and scope complexity. Software prices are list prices from vendor pages and AWS Marketplace, October 2026.
On these published figures, for an ISO-only program under 50 people, the certification body can cost as much as the software or more. Optimizing the software line while ignoring audit days and internal audit effort is the most common budgeting mistake.
FitWho should choose which
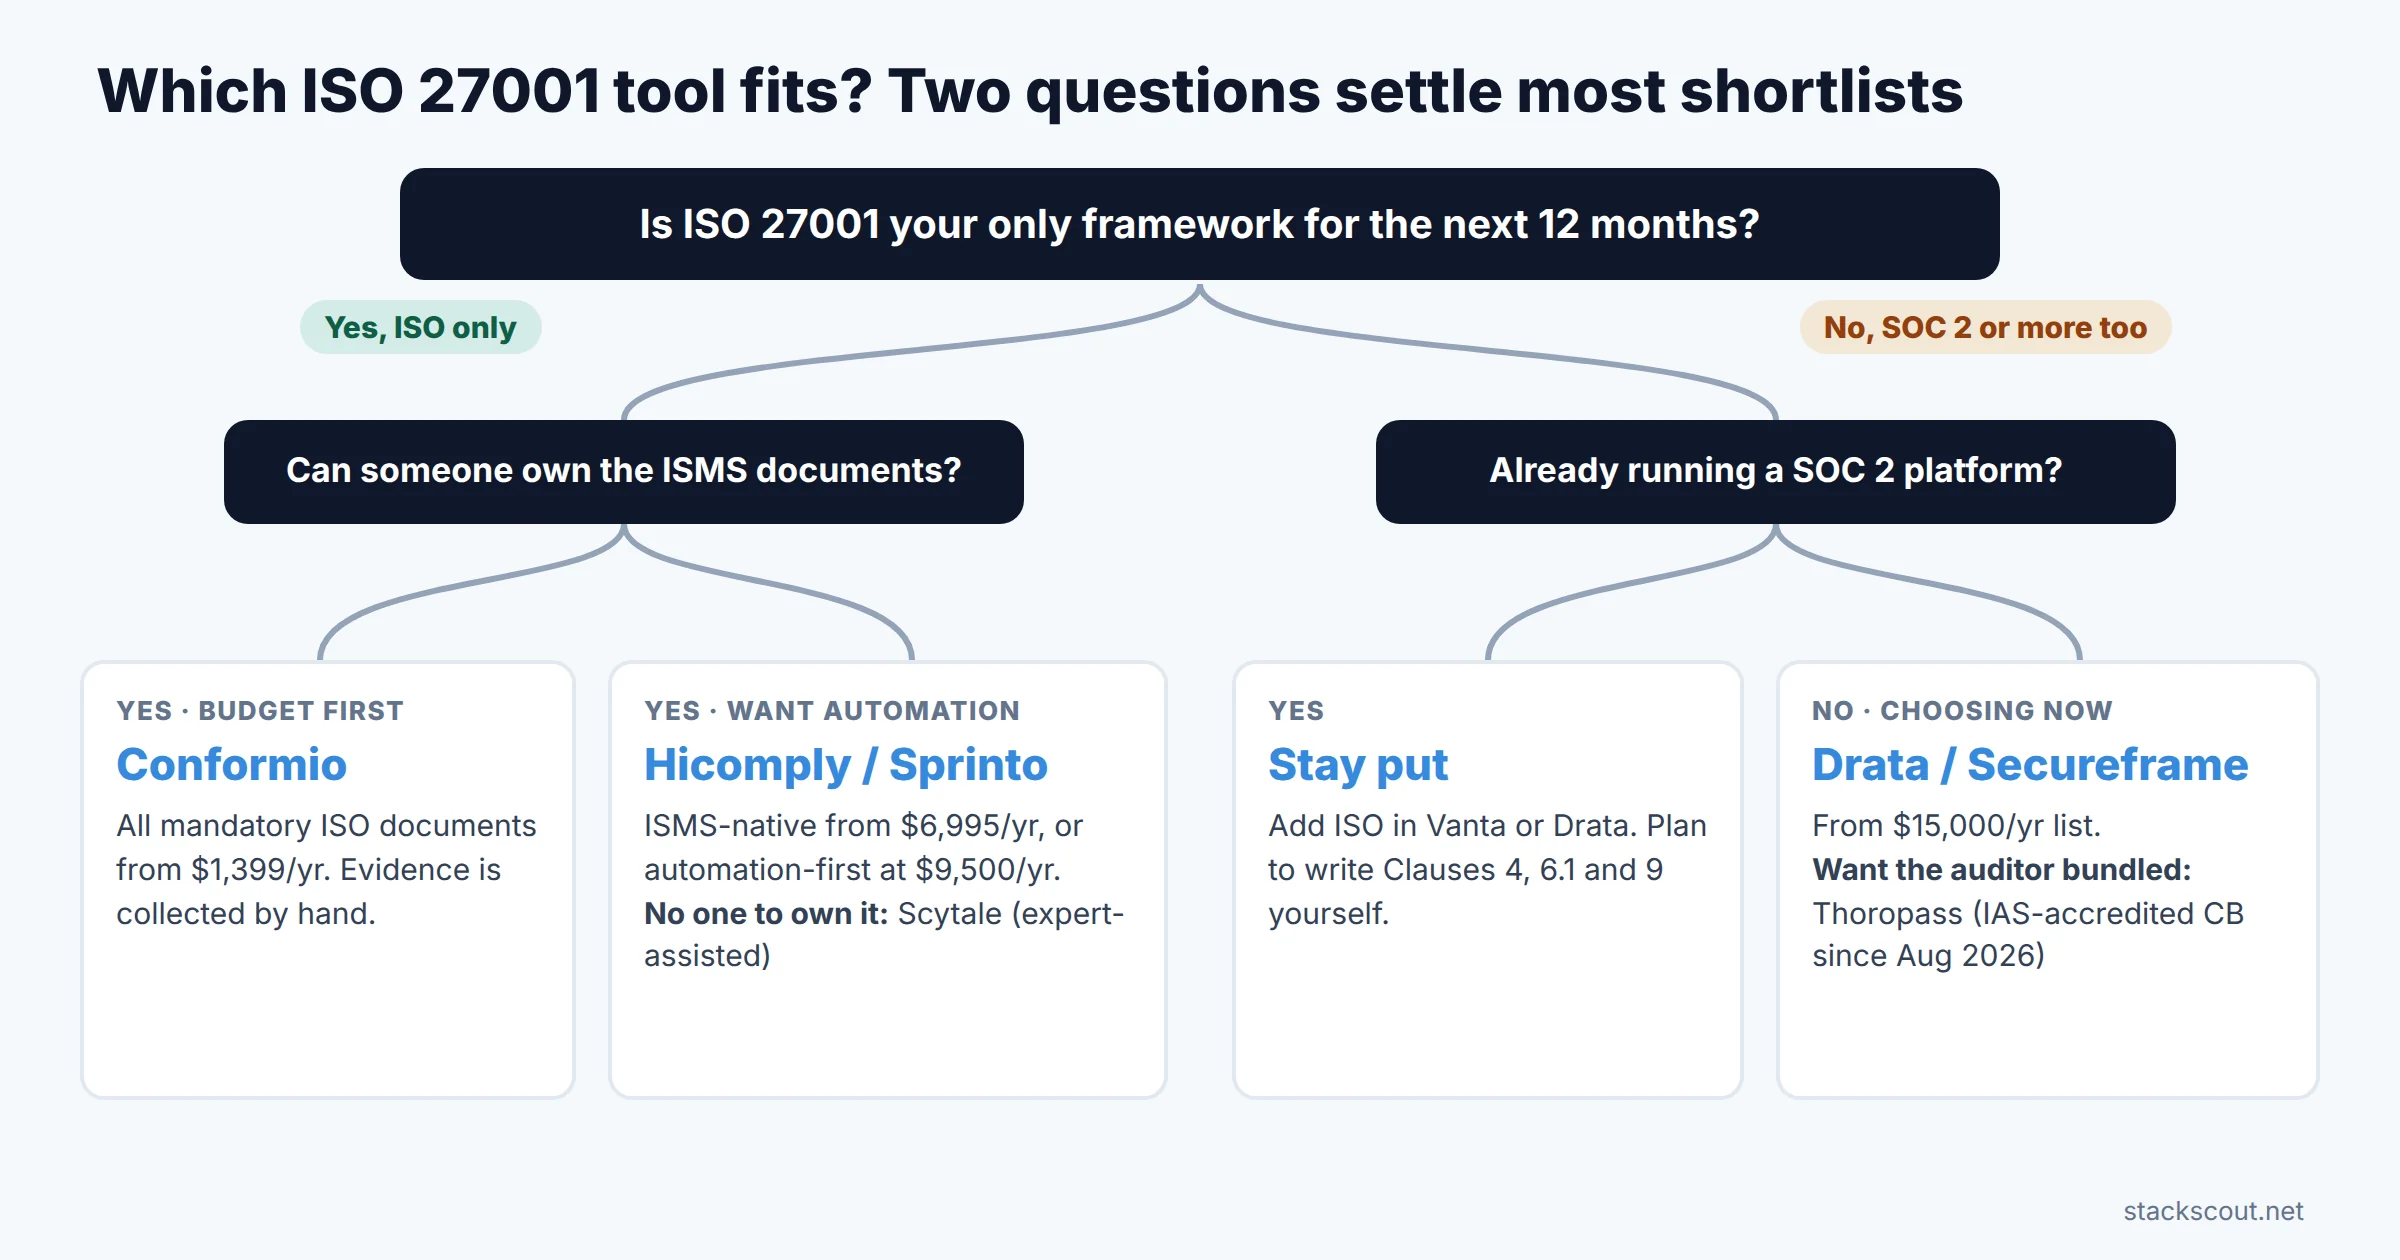
If you're still unsure how to weight these criteria for your own organization, our compliance automation decision framework walks through the scoring step by step.
MethodHow we chose
We started from the tools that appear most often in the current top search results for this query, then removed those with unresolved integrity concerns (Delve) or no ISO 27001-specific product. Each remaining tool was graded on four criteria, weighted toward what an ISO auditor tests: (1) ISMS documentation coverage for Clauses 4–10, including whether internal audit and management review records are supported; (2) risk assessment depth, from method to treatment plan to SoA linkage; (3) the certification-body route, including accreditation and impartiality; and (4) published price and what it includes. Feature claims come from each vendor's public product pages, help centers and pricing pages; prices from vendor pages and AWS Marketplace listings, checked October 22–23, 2026 (Thoropass, September 2026). We did not run hands-on trials of every platform, and no vendor paid for placement.
FAQFrequently asked questions
What is the best software for ISO 27001 compliance?
What is the best compliance management platform in 2026?
Is ISO 27001 outdated?
What is the newest version of ISO 27001?
Can my compliance software vendor also be my ISO certification auditor?
Sources
- ISO — ISO/IEC 27001:2022 (status, edition, accredited certification)
- Advisera — Conformio pricing and features
- Hicomply — Plans and pricing
- ISMS.online — Plans
- AWS Marketplace — Vanta
- AWS Marketplace — Drata
- AWS Marketplace — Secureframe
- AWS Marketplace — Sprinto
- AWS Marketplace — Scytale
- Vanta Help Center — Statement of Applicability
- Vanta Help Center — ISMS management review checklist
- Drata — ISO 27001 product page
- Secureframe — ISO 27001
- Sprinto — ISO 27001 guide
- Scytale — ISO 27001
- IAS — Thoropass Certification LLC accreditation certificate MSCB-422
- Thoropass — Impartiality and inquiries
- IT Governance — ISO 27001 certification costs (audit day table)
- usd AG — New requirements of ISO/IEC 27006-1:2024
- TÜV India — ISO/IEC 27006-1:2024 transition client information
- ISO Help — How to verify an accredited certification

Technology consultant with 10+ years in the Japanese tech industry. Specializing in SaaS evaluation, workflow automation, and B2B tool integration.